Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
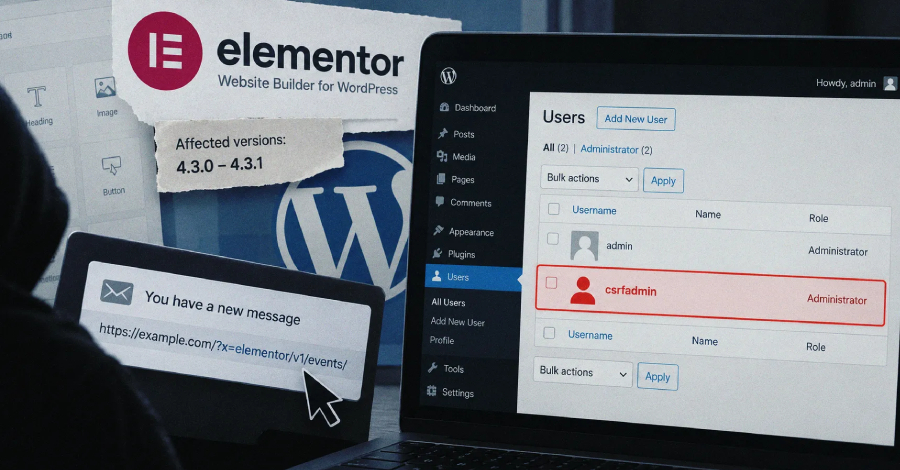
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site. The cross-site request forgery (CSRF) vulnerability, which has yet to be assigned a CVE identifier, carries a CVSS score of 8.8 out of 10.0. It only affects versions
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities in question are as follows – CVE-2026-65660 (CVSS score: 8.8) – A code injection vulnerability in Microsoft Office SharePoint
Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an imminent cyber attack. “Kiteworks received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some Kiteworks systems,” said Frank Balonis, Chief
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware
Two actions-cool GitHub Actions have been disabled for a second time after the repositories became accessible last week, months after they were compromised during the May 2026 Mini Shai-Hulud campaign. The affected GitHub Actions are listed below – actions-cool/issues-helper actions-cool/maintain-one-comment Visiting either of the repositories now shows the message: “Access to this
PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence
Cybersecurity researchers have flagged a new version of PamStealer that ensures that the main payload can only be recovered using a server-side decryption chain. The latest artifacts, per Jamf Threat Labs, continue to rely on the same JavaScript for Automation (JXA) dropper mechanism, but modify the lure and the delivery method. “Where earlier variants embedded their payload key material
Social Media Bans Aren’t Enough to Make Children Safe
Even before France approved legislation banning social media for children under 15 last January, 13-year-old Benjamin was already wondering what life without social media would look like. “If we want to play football, we won’t be able to organize it. What will we do? Send letters instead?” he joked in an interview for Le Monde. His reaction captured the central challenge behind the growing wave…
The SOC Doesn't Need to Start Over with Every Alert
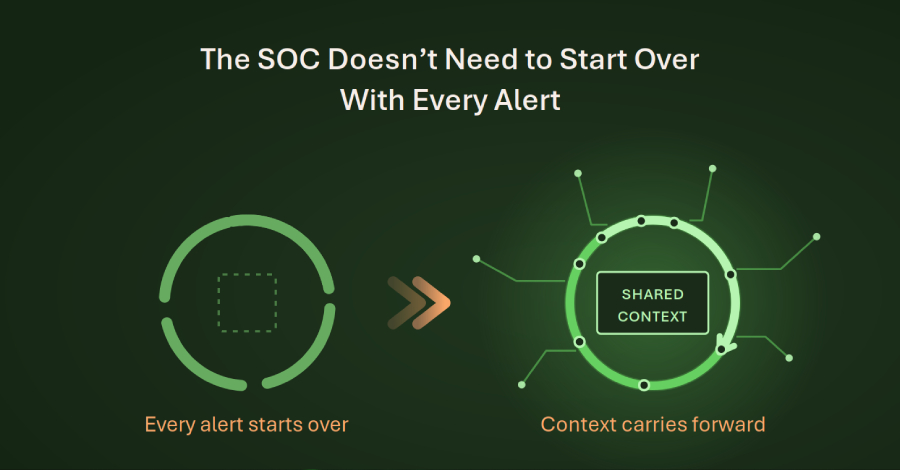
Security leaders keep debating whether AI will produce an entirely new class of cyberattack. The nearer change is quieter and already visible: AI has made a failed attack cheap to retry. The routine version looks like this. An attacker lands on a low-privilege cloud account, and the first try at privilege escalation goes nowhere. That dead end used to cost hours of documentation reading,
Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise
Cryptocurrency exchange Bitget said suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets. “At 18:31 UTC on September 24, 2026, Bitget’s security systems identified unauthorized transfers involving a limited number of hot wallets,” BitGet said in a post shared on X. “Bitget’s cold wallets and the overwhelming majority of platform assets remain
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild
The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild. The vulnerability in question is CVE-2026-48842 (CVSS score: 8.1), a pre-authentication SQL injection in the virtuser_query plugin of Roundcube Webmail versions 1.6.x before 1.6.16 and 1.7.x before 1.7.1. The issue stems from a preg_replace() backslash
Mexican EPICS in IEEE Team Builds Portable Educational Platform
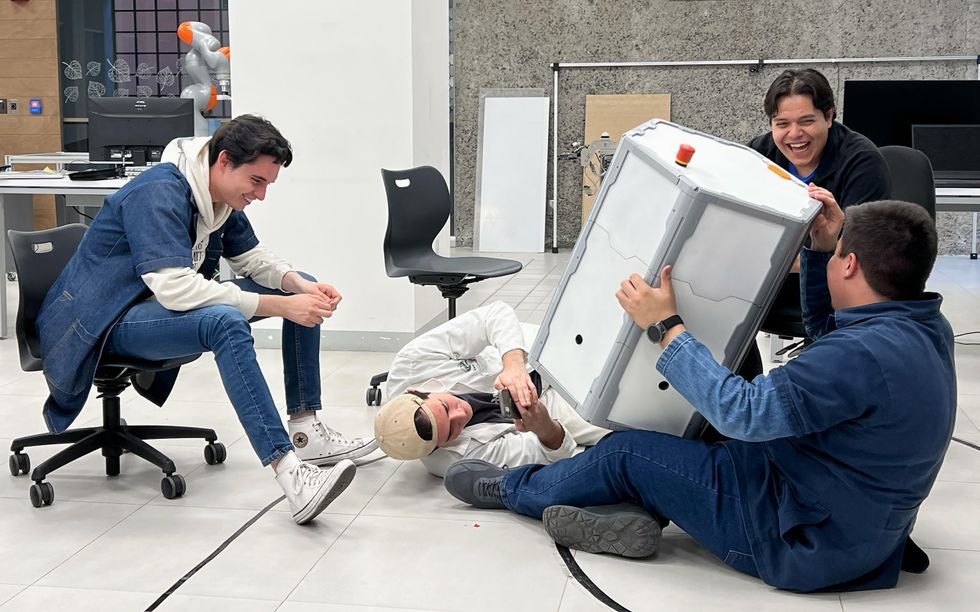
In Guadalajara, Mexico, many high schools have motivated teachers and talented students with an interest in science, technology, engineering, and mathematics, but they lack access to advanced tools such as robotics laboratories. The resources shortfall limits the students’ opportunities for hands-on learning on cutting-edge applications.A team from ITESO, Universidad Jesuita de Guadalajara, is…