Add Your Heading Text Here

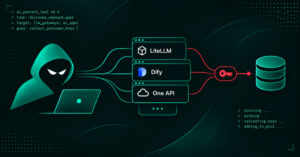
Amazon Uncovers AI Agent Campaign Targeting LiteLLM, Dify, and Other Apps for API Keys

Attackers’ AI agents have been hunting for weak spots in internet-exposed AI apps such as LiteLLM, One API, and Dify to steal the AI provider keys stored inside, according to the agents’ own records. The records, which Amazon’s threat intelligence team captured with decoy servers, describe stolen keys being used to run the AI models that powered the search for more keys. The team said this
Read More »

BO Team Exploits Log4Shell in VMware vCenter, Compromises Russian Firm's Code-Signing Server

An investigation into suspicious activity within a Russian software developer’s network has uncovered a months-long compromise of its development infrastructure and a software code-signing server. The activity, documented by Kaspersky’s ICS CERT team after it was contacted by the affected developer in June 2025, has been attributed to a threat actor named BO Team (aka Black Owl, Hoody Hyena,

Read More »

Italy Fines Meta €805 Million Over Facebook's Android Gallery Access Without Explicit Consent

Meta was fined €805 million in Italy yesterday over a Facebook for Android feature that suggests photos and videos from users’ phone galleries for them to post. The Garante, Italy’s data protection authority, found that the feature was enabled by default and that the app accessed Italian users’ photos, videos, and related metadata without their explicit consent. The company has 60 days to

Read More »

Cursor Says Stolen Fireworks AI Key Led to Trojanized Claude Code Extension Incident

The compromise of Anthropic’s official Claude Code extension on Cursor’s extension marketplace was the result of the theft of an access key that was exposed in the wake of a breach targeting Fireworks AI. “An attacker obtained an access key we had issued to Fireworks,” Cursor said in a Friday update. “The key was exposed by Fireworks, and the attacker used it to copy data from a read-only

Read More »

Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a high-severity security flaw impacting UnrealIRCd, an open-source Internet Relay Chat (IRC) server, to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-114713 (CVSS score: 8.6), is a case of improper neutralization of delimiters

Read More »

PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE

A type confusion flaw in PostgreSQL lets a database user who can create objects run code on the server. Updates released yesterday fix it, along with 51 other security flaws. Full protection from this flaw also requires rebuilding any C-language extensions installed on the server. The flaw, tracked as CVE-2026-6460, has a CVSS score of 8.8. Any code run this way has the rights of the operating

Read More »