The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and internet-facing infrastructure, security is shifting toward continuous visibility, control, and the ability to respond to risk at scale. This report examines how core areas of
GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers
A critical flaw in GitLab’s AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw is fixed in gateway versions 19.2.4, 19.3.2, and 19.4.1. The flaw
Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. Cisco Talos is tracking the cluster
Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below – CVE-2026-63688 (CVSS score: 10.0) – A missing authentication for critical function vulnerability in the csm-authorization-storage gRPC server that an
OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. “We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information,” a spokesperson for the company was quoted as saying. “Our investigation confirmed that these
Why CISOs Struggle to Answer the Board's Three Hardest Questions, and How to Fix the Report
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a spreadsheet to reconcile them. Someone else is turning that spreadsheet into slides. Then a board member asks three questions: How secure is the organization, overall? What is
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
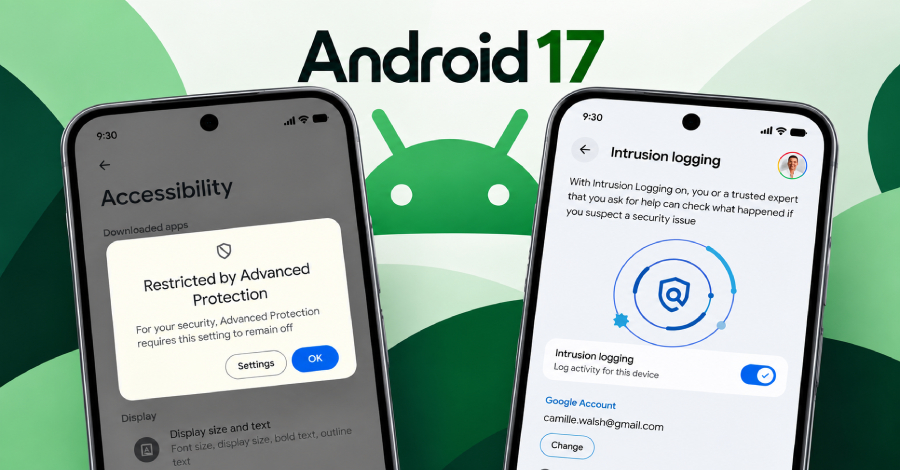
Google has announced a new security measure that limits access to Android’s accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a
Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
Two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway that allow remote code execution have been exploited in the wild, Citrix confirmed on September 27. It released fixes for both, along with six other flaws. One of the two affects every deployment on an affected version, including those in the default configuration. The bulletin came a day after security firm watchTowr
Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
Two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway that allow remote code execution have been exploited in the wild, Citrix confirmed on September 27. It released fixes for both, along with six other flaws. One of the two affects every deployment on an affected version, including those in the default configuration. The bulletin came a day after security firm watchTowr
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Psychedelic Stealer malware distributed via compromised Ukrainian websites using ClickFix-style Cloudflare verification checks is part of a wider malware-as-a-service (MaaS) platform called Lunex. The new findings come from Ontinue, which described the activity as a four-stage attack chain aimed at targeting Ukrainian-speaking users. “The attack chain begins with a fake CAPTCHA page and