Meet the new faculty members joining MIT Sloan in 2026
Debiased machine learning, the currency of invoicing, and training good models with bad data: Meet the new experts bringing their knowledge and skill sets to the MIT Sloan School of Management.
Opera GX Flaw Let Malicious Sites Auto-Install Mods to Steal Data From Visited Pages
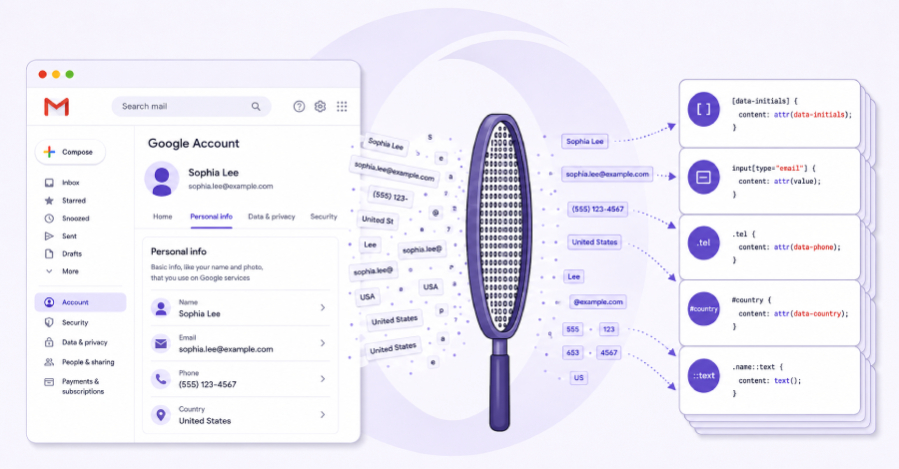
Researchers found a flaw in Opera GX, the gaming-focused version of the Opera browser, that let a malicious website silently install a browser add-on and use it to lift specific data from the pages a victim visits. In a proof of concept, they reconstructed a signed-in user’s full Gmail address from a single visit, with no click. Opera has patched the flaw and says it found no evidence that
SkillCloak Lets Malicious AI Agent Skills Evade Static Scanners with Self-Extracting Packing
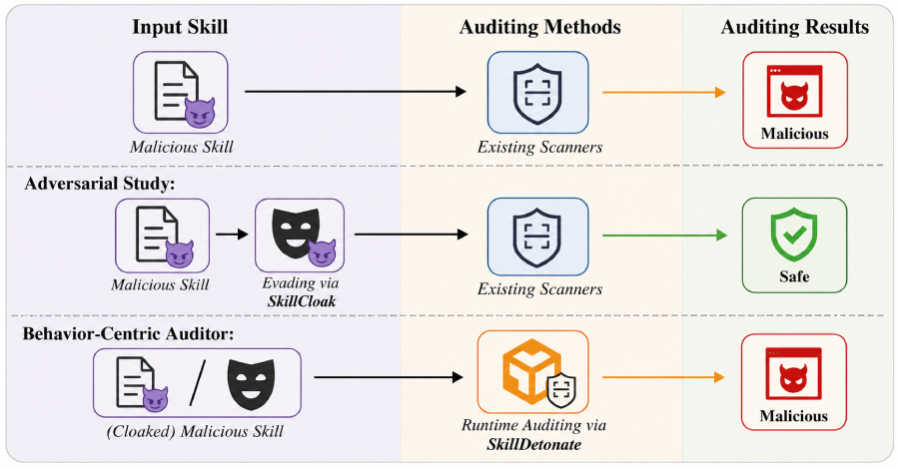
Scanners meant to catch malicious add-on “skills” for AI coding agents can be fooled by a few simple changes that leave the malware working, according to a new study from researchers at the Hong Kong University of Science and Technology. Their strongest trick slipped past every scanner tested more than 90% of the time, and the same team built a runtime checker that catches most of the
Data liquidity leads to AI success
Three levers — data architecture, data preparation, and data permissions — determine whether data becomes a reusable strategic asset or stays trapped in silos.
Public PoC Released for Critical libssh2 CVE-2026-55200 Client-Side SSH Flaw
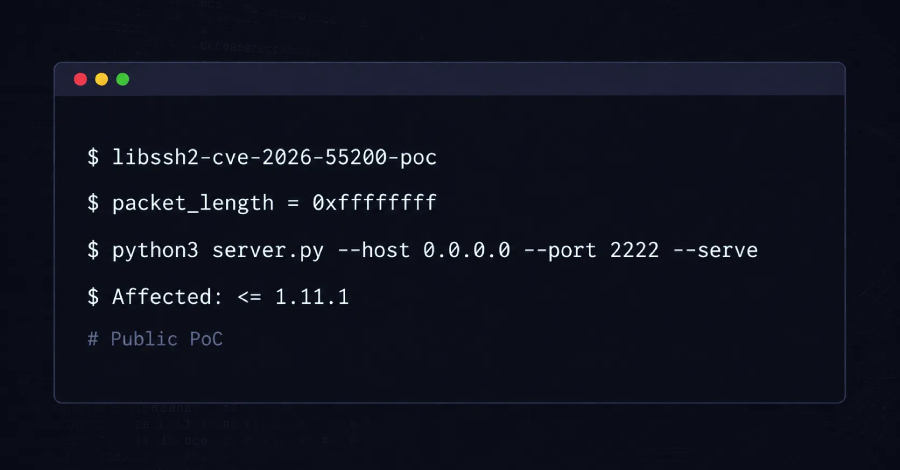
A public proof-of-concept is now out for CVE-2026-55200, a critical flaw in libssh2 that lets a malicious or compromised SSH server trigger memory corruption on a connecting client, with possible code execution. No credentials, no user interaction. The bug affects every release up to and including 1.11.1 and carries a CVSS 4.0 score of 9.2. libssh2 is a client-side SSH library, not a server.
Hijacked npm and Go Packages Use VS Code Tasks to Deploy Python Infostealer
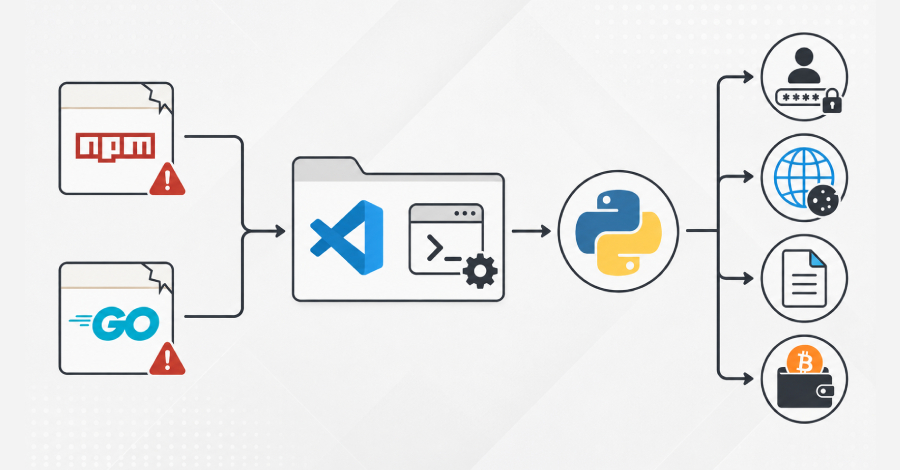
Cybersecurity researchers have uncovered two hijacked npm packages and a cluster of Go packages that are designed to deploy a Python-based information stealer on compromised Windows, Linux, and macOS hosts. “This attack avoids the most common npm execution paths through lifecycle scripts, perhaps in an attempt to remain ‘compatible’ with npm v12’s security hardenings,” JFrog said in a
Pro-worker AI, explained
Artificial intelligence can make workers more capable and productive, but only if leaders design and deploy it to augment human judgment.
5 things to consider when working with AI
Researchers at the MIT Initiative on the Digital Economy share the latest insights about getting the most from working with AI, such as personality pairing and reorganizing job tasks.
Balance AI innovation and risk with ‘minimum viable governance’
As organizations scale generative AI, traditional governance models prove to be too rigid or too loose. Minimum viable governance calibrates oversight to risk, enabling responsible innovation.
Canada’s Spy Agency Used First-of-Its-Kind Warrant to Clean Botnet-Infected Devices
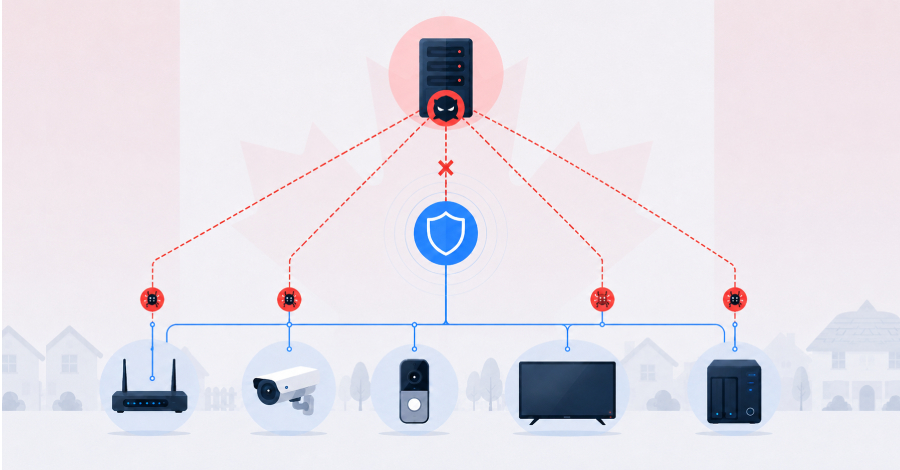
Canada’s spy service got a judge’s permission to reach into infected servers, home routers, and IoT gear sitting on Canadian soil and neutralize two foreign-run botnets. The Federal Court released a public version of the ruling on June 15. It is the first time the Canadian Security Intelligence Service has used its threat reduction warrant powers this way. The warrant let CSIS alter,