AryStinger Malware Infects 4,300 Legacy Routers to Build Reconnaissance Proxy Network
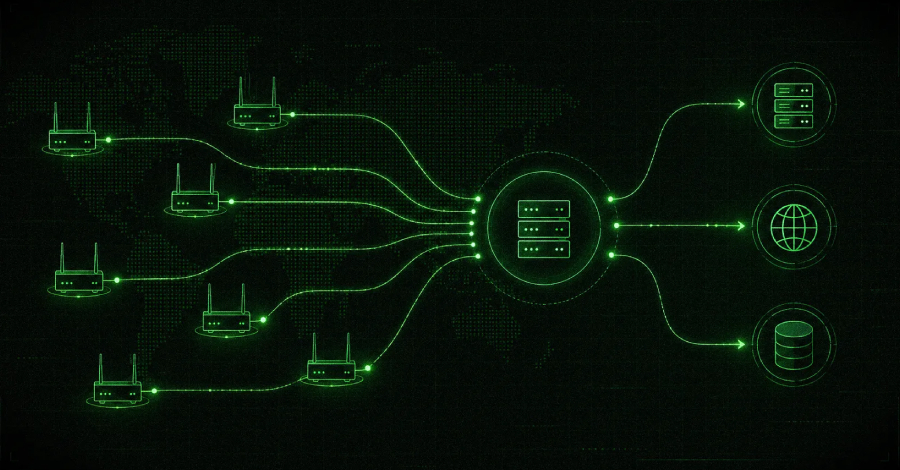
A new malware family is turning forgotten home routers into a distributed reconnaissance and proxy network, not the DDoS botnet these devices usually end up in. QiAnXin’s XLab calls it AryStinger and counts at least 4,300 infected routers, a total it says is still rising. The distinction matters. AryStinger exists for the stage of an attack that comes before the break-in. Infected
INTERPOL Warns Phishing, Ransomware, and AI Scams Are Rising Across Asia-Pacific
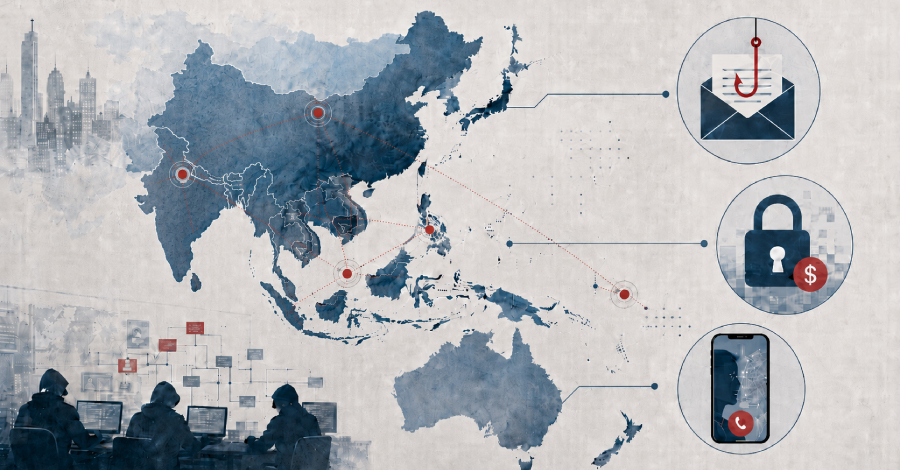
A new report from INTERPOL has revealed a “dramatic increase” in cybercrime in Asia and the South Pacific, fueled by rapid digitalization, internet penetration, new technologies, organized criminal networks, and a disparity in cybersecurity maturity. According to INTERPOL’s 2025/2026 Asia and South Pacific Cyberthreat Assessment Report, phishing has emerged as the most widespread and
The surprising power of warmth in AI negotiations
In MIT’s international AI Negotiation Competition, “warmer” agents achieved better outcomes in negotiations with other AI agents.
Seeing real value from AI depends on being able to verify its outputs
A new paper explores how seeing economic value from artificial intelligence hinges on closing the gap between what AI can do and how humans can verify its outputs.
Sniper Dz Scams Target MENA Users via Fake Facebook Offers and Browser Alerts
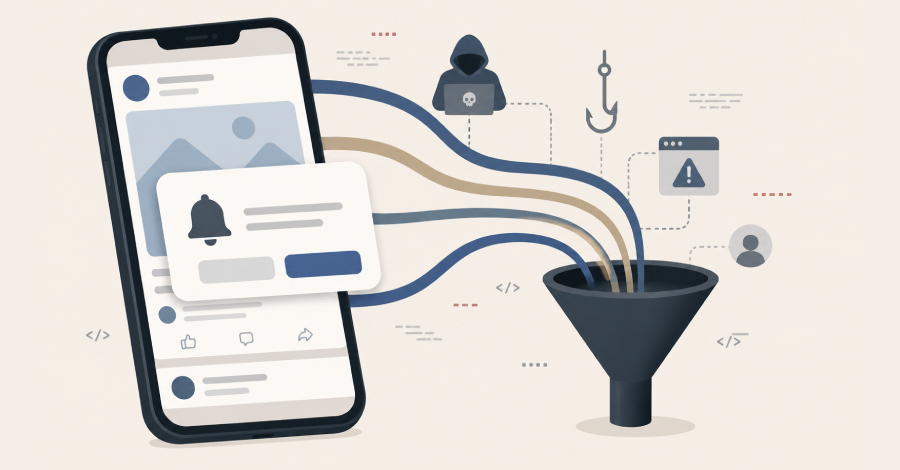
Cybersecurity researchers have disclosed details of fraudulent activity targeting users across the Middle East and North Africa by employing various fraudulent Facebook accounts impersonating politicians, public figures, and trusted organizations. “These accounts promoted fake offers, including free mobile internet packages, financial compensation, and government subsidy programs,” Group-IB
Palo Alto Warns of Active Exploitation of PAN-OS GlobalProtect VPN Flaw
Palo Alto Networks has revealed that it has observed “active exploitation” of a recently disclosed PAN-OS vulnerability by an unknown threat actor to obtain unauthorized access to GlobalProtect portals. The vulnerability in question is CVE-2026-0257 (CVSS score: 7.8), an authentication bypass flaw affecting the portal and gateway components of PAN-OS software that could be exploited by bad
‘AI gravity’ is pulling you toward dependency. Here’s how to push back
AI systems hold the promise of competitive advantage, but they can usher in cognitive decline among workers, says MIT Sloan School of Management’s Eric So. Learn how to protect cognitive capital.
Heeding the pope’s call to ensure AI protects human dignity
Following Pope Leo XIV’s encyclical on AI, MIT Sloan professor emeritus Thomas A. Kochan argues that firms should partner with workers to ensure AI augments human skills and knowledge.
UNC3753 Used Vishing and Physical Intrusions in U.S. Data Theft Extortion Campaign
Cybersecurity researchers have disclosed details of a financially motivated data theft extortion campaign that has targeted dozens of organizations across professional, legal, and financial services in the U.S. between January and May 2026. The activity has been attributed by Google Mandiant and Google Threat Intelligence Group (GTIG) to a threat actor dubbed UNC3753, which is also known as
VS Code Adds 2-Hour Extension Auto-Update Delay to Limit Supply Chain Attacks
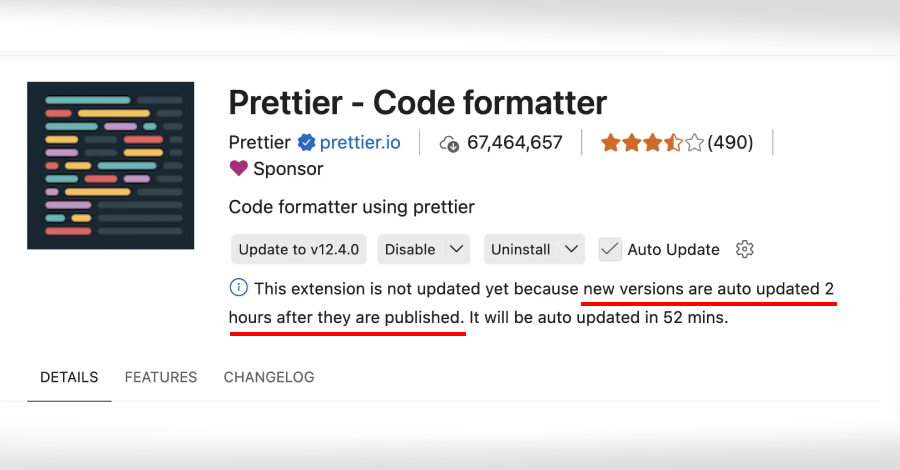
Microsoft has announced that Visual Studio Code (VS Code) will apply a two-hour delay before extensions for the integrated development environment (IDE) are updated automatically to a newer version in an attempt to tackle software supply chain threats. “When automatic updates are enabled, new versions are auto-updated two hours after they are published, adding an extra layer of protection